Turn CRA compliance into a process that runs every day
The CRA asks two things of every product. Shield Lifecycle covers both.
- Before the sale: the evidence for the CE marking
- After the sale: every new vulnerability checked, exploited ones reported, until the end of support
Your machine runs software. EU law makes you responsible for its security.
- 11 Sep 2026 In force CRA reporting duty Report actively exploited vulnerabilities and severe incidents within 24 hours. It also covers products already on the market.
- 20 Jan 2027 105 days left Machinery Regulation applies Cybersecurity becomes an essential health and safety requirement for CE marking of machines.
- 11 Dec 2027 430 days left CRA applies in full Every new product with digital elements needs an SBOM, vulnerability handling and security updates.
Each date links to its regulation, with the official text. All three side by side.
Same model, same customer. One machine is exposed, the other is not.
A critical vulnerability hits a VPN gateway. One X-200 has it and drops to 68. The other was delivered with a different gateway and stays at 90.
- PLC FW 2.9
- HMI FW 17.0
- GW-A FW 2.4
- TLS 3.0.x
- Linux 5.15-rt
GW-A 2.4 is inside and can be reached through remote maintenance.
- PLC FW 2.9
- HMI FW 17.0
- GW-B FW 5.1
- TLS 3.0.x
- Linux 5.15-rt
Delivered with GW-B. The CVE does not apply.
Which one are you?
Your machines run software you did not write
When a component has a vulnerability, you must know which delivered machines are exposed and tell the customer.
Keep every machine CRA-ready
A 24-hour reporting duty, and no security team
The CRA asks for an SBOM, vulnerability handling and fast reporting, every day.
See what the CRA asks
Segment the OT network without stopping production
Old machines, flat networks and auditors who ask for NIS2 and IEC 62443 evidence.
Segment on the switches you havePhotos generated with AI.
Find what is exposed. Protect it. Prove it.
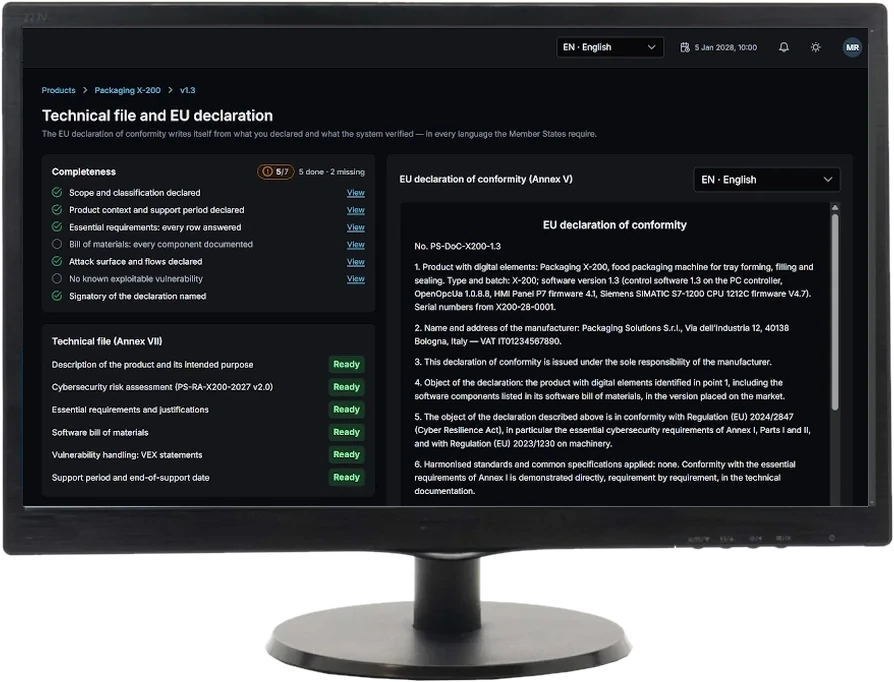
Shield Lifecycle
Know every day which machines you shipped are exposed to a new vulnerability, and tell your customer in time.
Explore Shield Lifecycle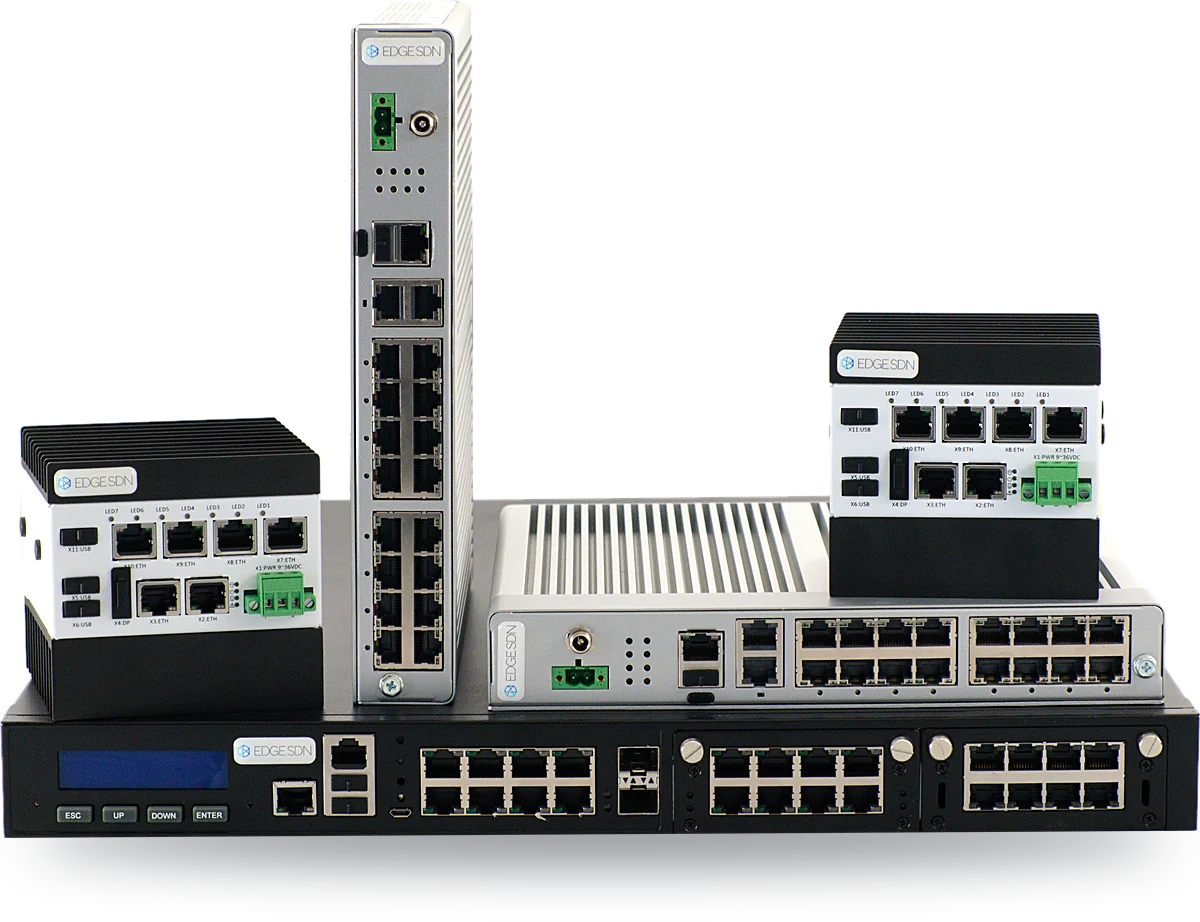
Edge Shield
Reduce the attack surface of the machine. Micro-segment and inspect its traffic, without touching the network or the PLC program.
Explore Edge Shield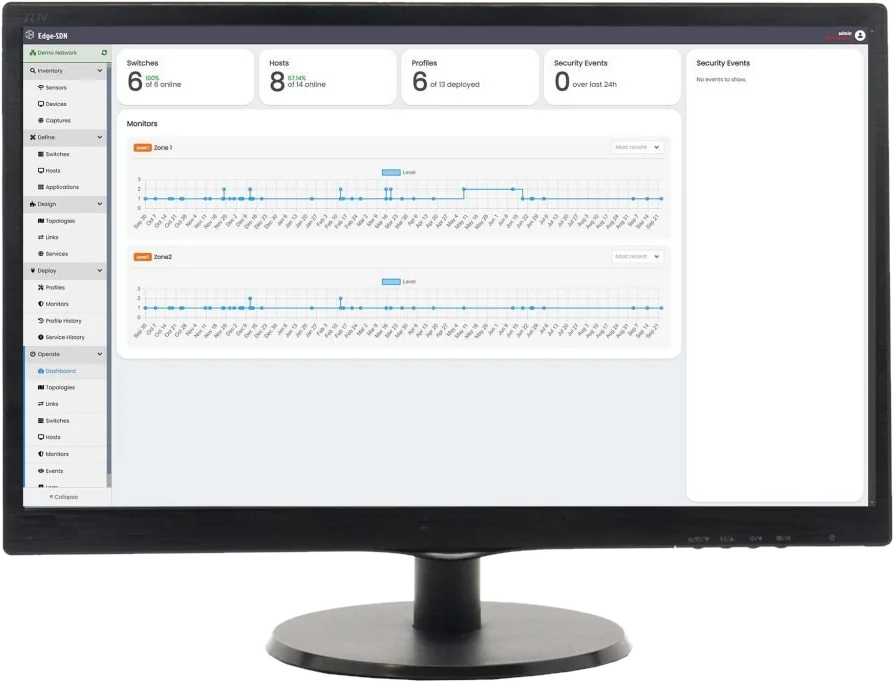
Edge SDN
See and segment the whole OT network from one console, without stopping production.
Explore Edge SDN
Talk to us
Tell us who you are and what you need. We answer fast, usually within one working day.
Meet us at 35.BI-MU, fieramilano Rho, 13–16 October 2026
Background photo generated with AI.