Segment the OT network on the switches you already have
Edge SDN finds what is exposed in your IT and OT network and protects it. Micro-segmentation of devices and communication, with no IP change, no VLAN change and no new firewall.
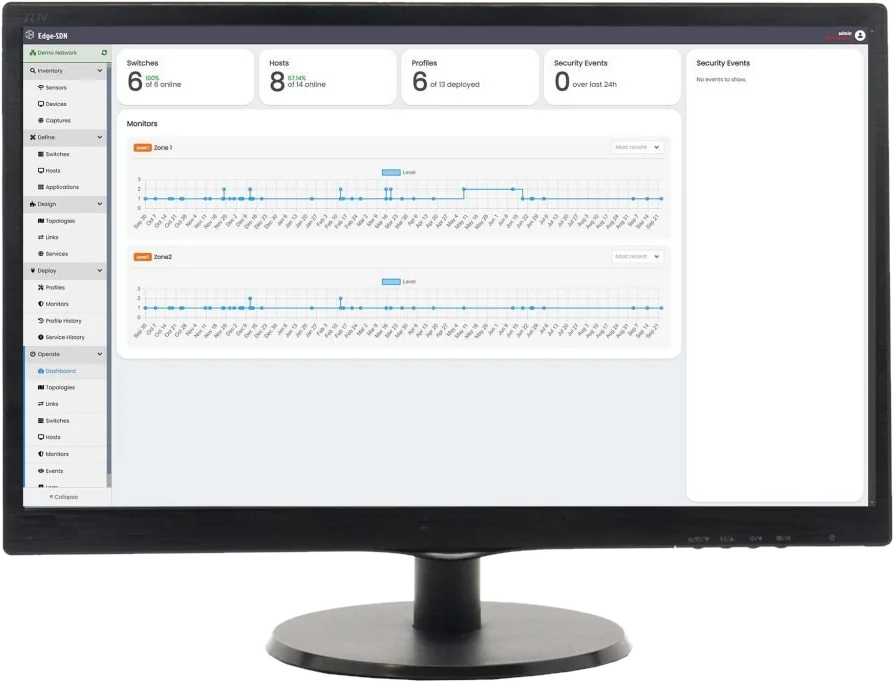
A security cycle that runs every day
Each step feeds the next. The longer it runs, the more accurate it gets.
- Probe
Discover
OT-safe scanning for asset inventory and passive probe for traffic analysis and IDS.
- Console
Assessment
A complete overview of the vulnerabilities, with a full risk analysis and a detailed view of communications between networks and to the Internet.
- Console
Protection design
Security zones, conduits and profiles for production, maintenance and backup, each with its risk.
- Your switches
Enforce
Micro-segmentation applied on the switches you already have.
- 24/7
Monitor
Current risk against residual risk, timeline and alerts. Information for your SOC.
- Reports
Prove
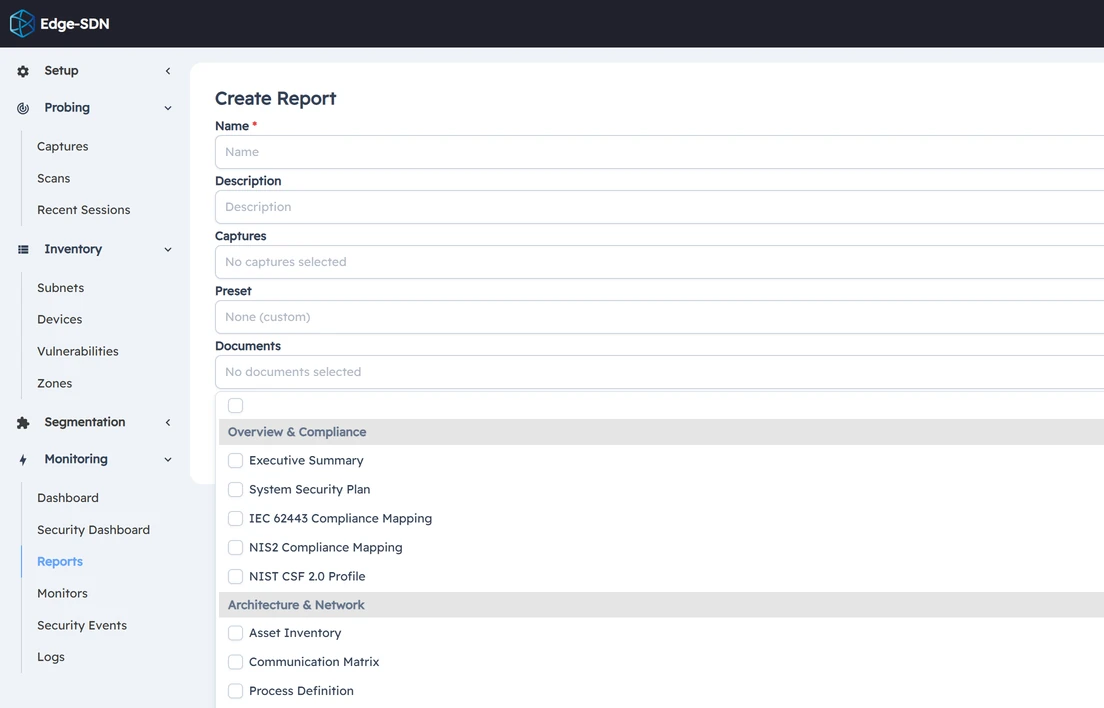
Reports and statistics that keep the evidence of how you manage security. NIS2, IEC 62443, NIST CSF, NIST SP 800-82.
Protection on the network you already have
- No IP changeEvery device keeps its address.
- No VLAN changeThe network design stays as it is.
- No new firewallSegmentation runs on the switches.
- Your switchesCisco, Aruba, HPE, Allied Telesis, OpenFlow 1.3, Edge Shield.
Through OpenFlow, NETCONF/YANG, REST API or CLI over SSH. More switch vendors are coming.
Network segmentation changes with a click
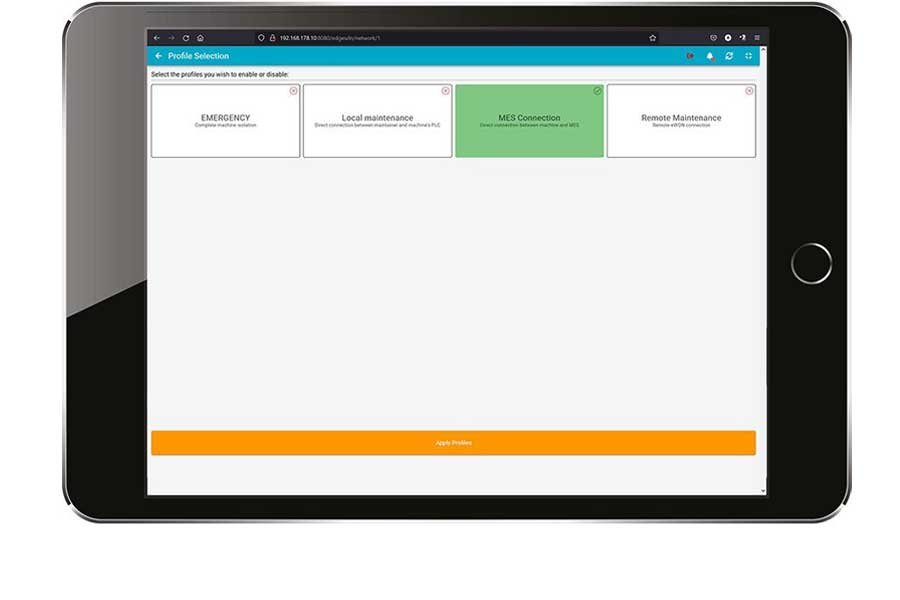
Profiles enable or disable network segmentation, internet communications, maintenance, protection of end-of-life devices, IEC 62443 security zones and conduits.
- A ticket to IT to open the firewall
- Hours or days of waiting
- Rules often too wide
- Rules left open afterwards
- No audit trail
- OT activates "Maintenance L2" from a tablet
- Only Line 2 opens, at once
- Precise rules, designed in advance
- Off again with one tap
- Full log with user and time
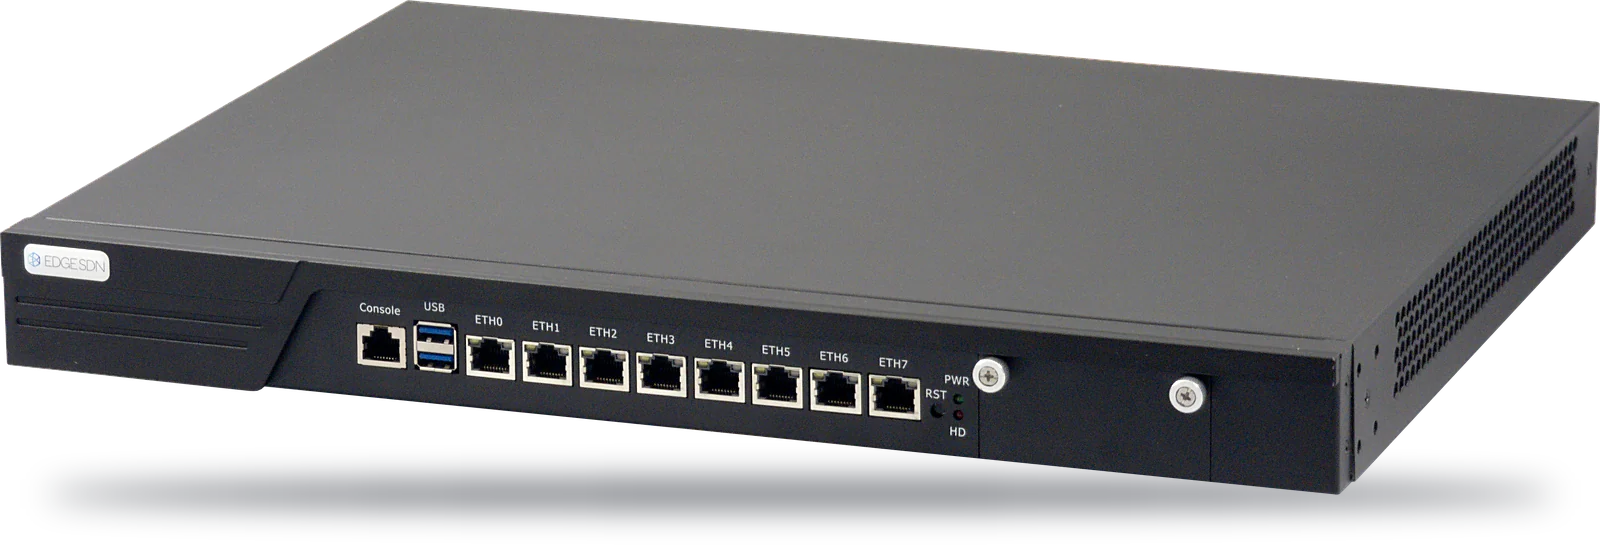
One hardware, two probes
Installed in your plant, rack 1U. The software makes it Standard or Advanced.
- Passive traffic analysis
- Communication between security zones
- IDS with IT and OT rules
- Everything in Standard
- Active, OT-safe asset inventory
- Vulnerabilities with CVE, CVSS and KEV
Keep the evidence for your audits
Edge SDN keeps the reports and statistics that document how you manage security: asset inventory, vulnerabilities, communication matrix, IDS events, risk before and after segmentation, and the history of every profile.
The reports support your audit. They do not replace it.
Where it helps you
- Built for itNIS2Directive (EU) 2022/2555
Segmentation and access control; asset inventory and vulnerability scanning with the Advanced probe; IDS for incident handling; NIS2 reports as evidence. Article 21(2)(a), (b), (e), (i)
- Built for itIEC 62443Standard series
Plant-wide zones and conduits, restricted data flow, monitoring, asset inventory with the Advanced probe; IEC 62443 reports as evidence.
- Built for itNIST SP 800-82Guide to OT security
Defense in depth and segmentation, OT asset inventory and monitoring.
- Built for itISO/IEC 27001Standard
Network security and segregation; inventory and technical vulnerabilities with the Advanced probe; monitoring.
- Built for itNIST Cybersecurity Framework 2.0Framework
Identify with the Advanced probe, Protect, Detect.
Questions about Edge SDN
Do I have to replace my switches?
No. Edge SDN applies micro-segmentation on Cisco, Aruba, HPE and Allied Telesis switches, on any SDN switch compatible with OpenFlow 1.3 and on Edge Shield units. More vendors are coming.
Will segmentation stop my production?
No. Every activity is planned, authorised and supervised. The segmentation runs on the existing switches, so IP addresses and VLANs stay as they are.
Can it run without an internet connection?
Yes. The console runs on-premises, on two virtual machines. Updates can come through an internal staging server, with no outbound connection.
What happens if the console goes offline?
The switches keep the segmentation that was applied. A break-glass procedure restores communication in an emergency.
Can Edge SDN feed our SOC?
Yes. Alerts, events and network information reach your SOC or SIEM through Syslog and REST API.
Who uses it, IT or OT?
Both. IT designs the zones and the profiles. OT activates a prepared profile from a tablet, when production needs it.
Last updated
See your OT network as it really is
In a first call we look at your network, the switches you have and the zones you need. You leave with a first outline of the zones and the next steps.
Meet us at 35.BI-MU, fieramilano Rho, 13–16 October 2026