Reduce the attack surface and the visibility of vulnerabilities
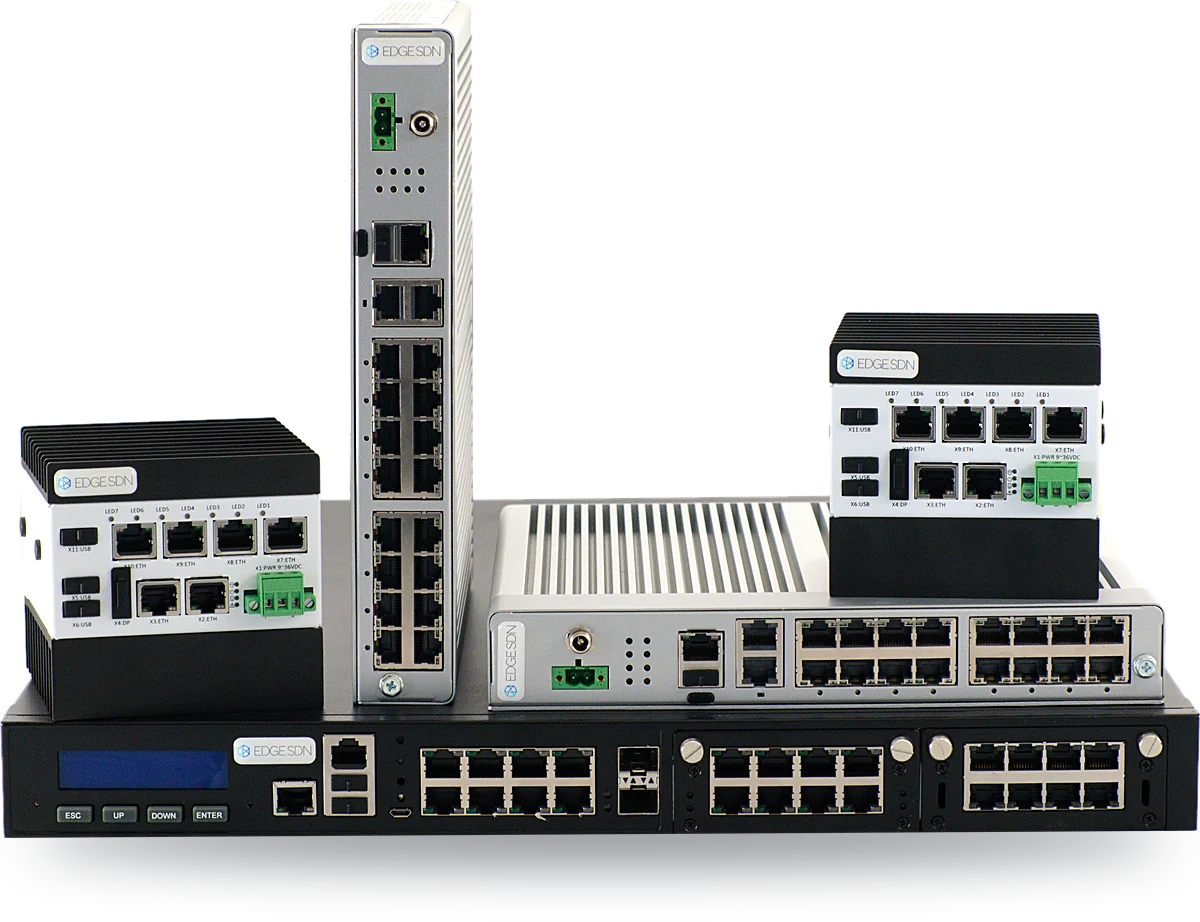
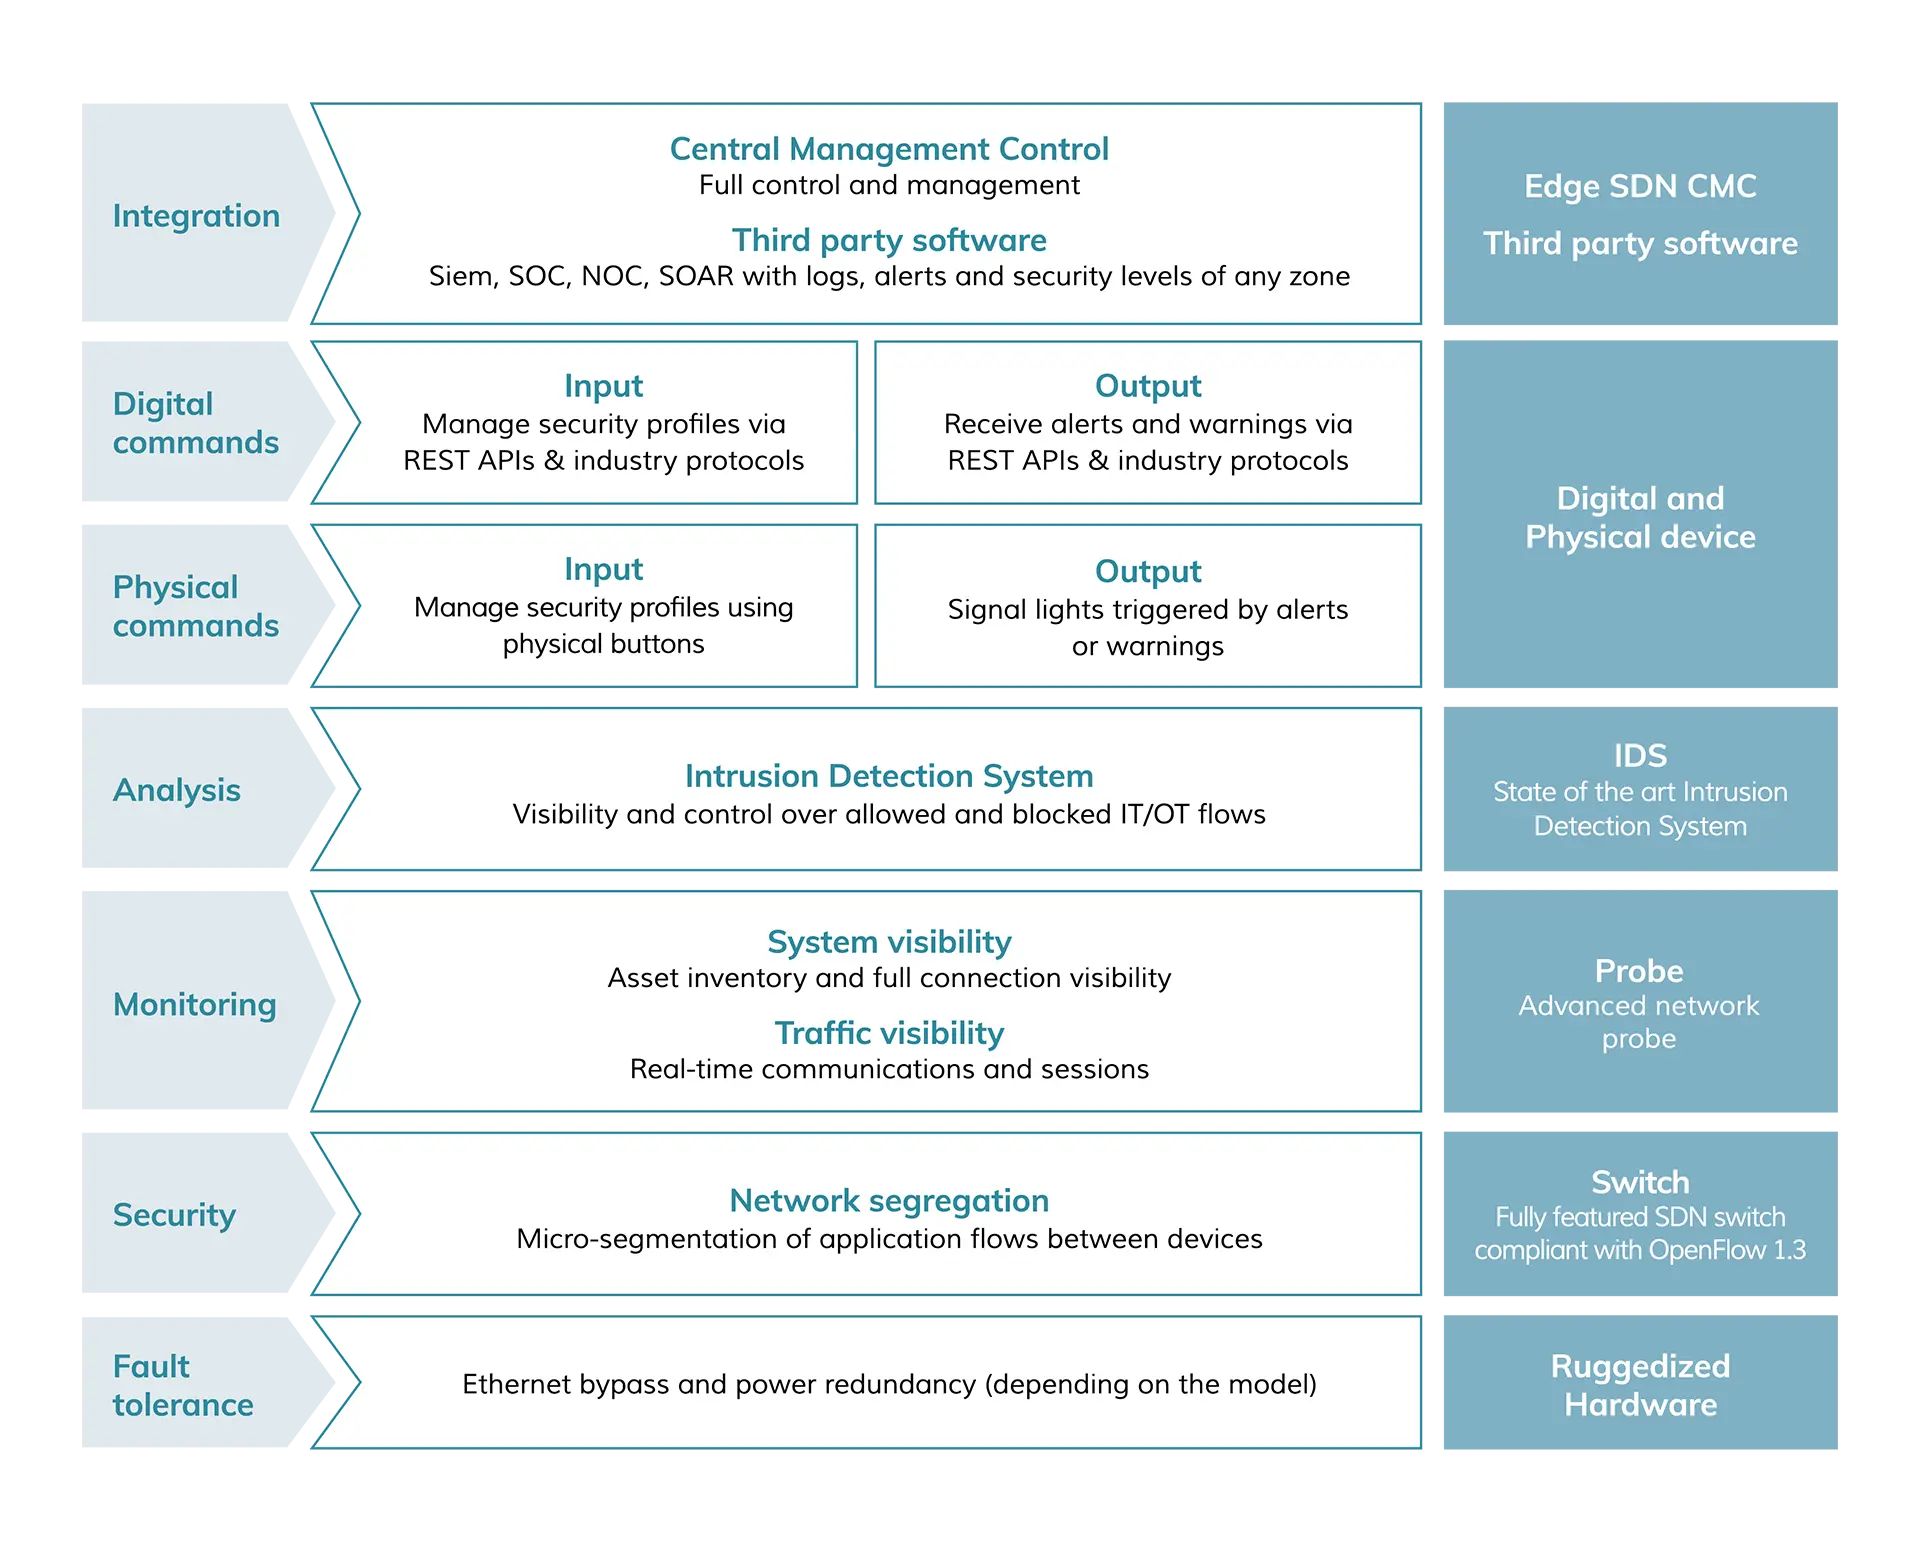
Edge Shield is a smart switch with a network probe and an intrusion detection system inside. Edge Shield protects a network portion by micro-segmenting the communication, while it inspects the traffic for malicious activity.
A switch, a network probe and an intrusion detection system.
See
Traffic analysis displays the paths that data takes through the network, and the unexpected traffic. It unveils the communication that business continuity depends on.
Isolate
Every device and application is isolated from the rest of the network. Every packet is identified and validated before it reaches a micro-segment, so each data flow runs on its own path.
Inspect
Edge Shield analyses the traffic to detect attempts to exploit vulnerabilities. Every communication at the edge of the network is monitored, with care to avoid false positives.
Integrate
Physical or digital controls and standard third-party software. Switch security profiles with push buttons or the REST API. Send alerts to industrial signal lights or to your software.
Your network
Protect your network at any layer
Add device visibility and protection without touching the current network configuration. Edge Shield is a standard SDN layer 2 switch, transparent to the current VLANs, IP addressing and routing.
Operating profiles
The machine has different states. So does its protection.
In production the machine talks to the MES and to telemetry, and nothing else. During remote maintenance a VPN toward the supplier opens for a limited time.
Each state is a profile with its own allowed flows and its own target Security Level according to IEC 62443. IT designs the profiles. The operator applies them with a button.
Old machines
Protect what you cannot patch
A machine installed fifteen years ago may run an operating system that no longer receives updates. Edge Shield closes what it does not need, with a unit sized for one machine.
The Edge SDN console manages many Edge Shield units and the rest of the network. Shield Lifecycle uses the profiles as the attack surface of the machine: a blocked path turns a vulnerability into a mitigated one.
Isolates machines that cannot be patched; its IDS helps incident handling. Article 21(2)(b), (e)
Helps with a part
IEC 62443Standard series
Zones and conduits for a single machine, a target Security Level per profile, IDS.
Helps with a part
NIST SP 800-82Guide to OT security
Segments and watches legacy devices.
Helps with a part
ISO/IEC 27001Standard
Segregation of single machines, monitoring with the IDS.
Helps with a part
NIST Cybersecurity Framework 2.0Framework
Protect and Detect for single machines.
FAQ
Questions about Edge Shield
Do I have to change IP addresses, VLANs or the PLC program?
No. Edge Shield works as a layer 2 switch and is transparent to the existing VLANs, IP addressing and routing. You do not touch the configuration of the network or of the machine.
What happens if the Edge Shield fails?
The P16 has 8 pairs of bypass ports and the M3 has bypass on 2 segments, designed to keep traffic flowing if the unit stops. The M3 also has redundant power supplies. Ask us which model fits the availability needs of your line.
Can the machine operator change the security profile?
Yes, in a controlled way. The IT administrator defines the profiles. The operator applies one with a physical push button or a digital one, for example to open remote maintenance for an hour. A REST API is also available, and alerts can drive an industrial signal light.
Do I need the Edge SDN platform to use Edge Shield?
No. Edge Shield can work on its own or together with third-party SDN switches. With the Edge SDN console you manage many units and the whole network from one place.
How does Edge Shield help with old machines?
A machine with an old operating system and open ports often cannot be patched. Edge Shield lets only the declared flows reach it and inspects them. Everything else is blocked. The machine keeps working and its exposure drops.
Can we sell Edge Shield with our own brand?
Yes. Hardware and software can carry your brand, so you deliver the protection with your machine, under your name.
Last updated
Show us the machine. We show you how to protect it.
Tell us which machine or cell you need to protect. We suggest the model, the profiles and the way to install it in a normal maintenance window.